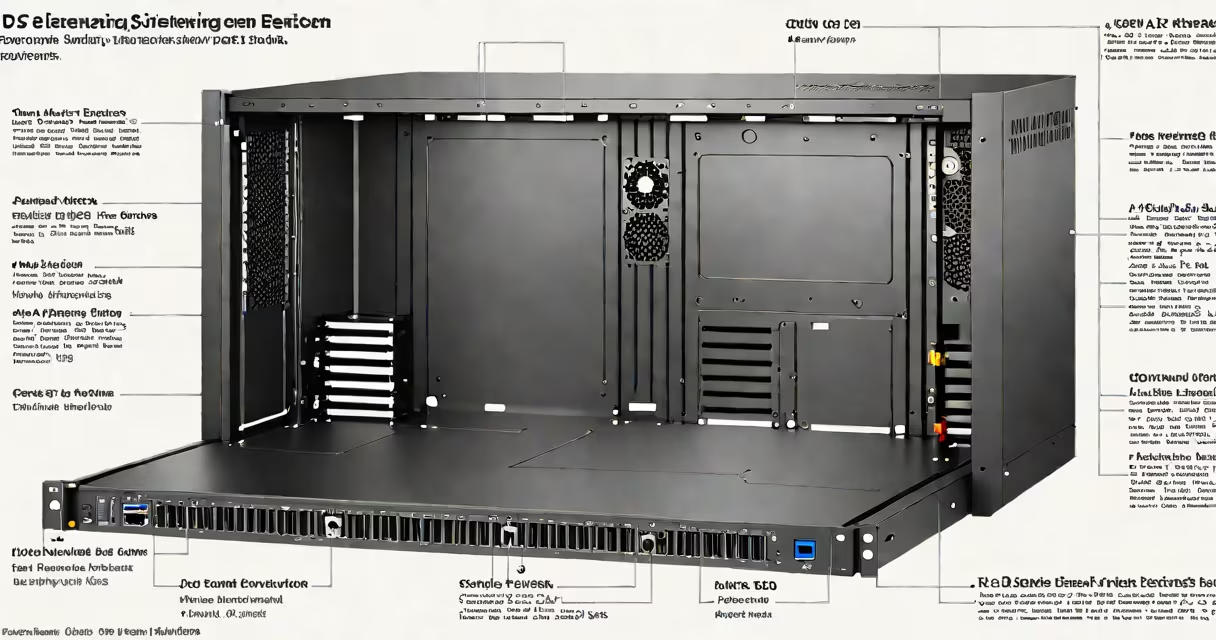
The F5 6000J3238G32GX2 TZ5N is a physical, rack-mounted application delivery controller (ADC) designed for large-scale enterprise environments. It delivers advanced traffic management, SSL offloading, and security functions within complex IT infrastructures.
This model is part of F5 Networks' BIG-IP platform, which integrates application delivery, load balancing, and threat protection into a single system. It supports up to 10 Gbps of throughput and handles thousands of concurrent connections, making it suitable for mission-critical applications such as e-commerce platforms, financial transaction systems, and cloud-based services.
Manufactured by F5 Networks, the 6000J3238G32GX2 TZ5N runs on the BIG-IP operating system, allowing centralized policy management via the F5 iControl REST API. It includes dual power supplies, redundant fans, and support for multiple network interfaces, ensuring high availability in production settings.
The F5 6000J3238G32GX2 TZ5N operates by intercepting incoming traffic and applying predefined rules to direct requests to the most appropriate backend server. It uses layer 4-7 inspection to analyze packets based on protocol, port, URL path, and HTTP headers.
For example, when a user accesses a banking website, the appliance checks the request's origin, encrypts the session using TLS, and routes the traffic to a server handling authentication. If that server fails, the ADC automatically redirects traffic to a backup server, maintaining uptime.
It also performs SSL termination, decrypting encrypted traffic before forwarding it to internal servers. This reduces CPU load on backend systems and enables deeper inspection for malware or data exfiltration attempts.
The F5 6000J3238G32GX2 TZ5N features:
It supports deployment in active-active or active-passive configurations. In active-active mode, both units share traffic processing, doubling capacity and providing automatic failover if one unit fails.
Configuration is done through a web-based GUI or command-line interface (CLI). Policies are created using iRules, a scripting language that allows custom logic for traffic routing, header modification, and access control.
Enterprises deploy the F5 6000J3238G32GX2 TZ5N to secure and improve access to internal applications. A major U.S. insurance provider uses it to route claims processing traffic between regional data centers, reducing latency by 40% during peak hours.
Financial institutions use it to enforce multi-factor authentication policies and detect anomalous login patterns. One bank reported blocking 12,000 attempted brute-force attacks per month after enabling bot detection and rate limiting on the device.
It is also used in hybrid cloud setups. A healthcare organization deployed it as a reverse proxy between public internet endpoints and private EHR (electronic health record) systems, ensuring HIPAA-compliant data flow and encryption at rest and in transit.
The F5 6000J3238G32GX2 TZ5N is often mistaken for a firewall or a load balancer alone. It is neither. While it includes stateful packet filtering capabilities, its primary function is application-layer traffic orchestration. A firewall blocks or allows traffic based on IP and port; this device makes decisions based on application content.
Another misconception is that all F5 appliances are software-only. The 6000J3238G32GX2 TZ5N is a physical appliance with fixed hardware specs. It cannot be virtualized or run on generic x86 servers. Its performance is tied to specific silicon and cooling design.
A non-obvious fact: the device ships with a default configuration that disables all unused ports and applies a minimal rule set. This prevents accidental exposure during initial setup. A misconfigured port left open can allow unauthorized access to internal APIs, leading to data breaches.
Here's how the 6000J3238G32GX2 TZ5N compares to other F5 BIG-IP models:
| Model | Throughput | Max Connections | Use Case | Form Factor |
|---|---|---|---|---|
| F5 6000J3238G32GX2 TZ5N | 10 Gbps | 1.2 million | Enterprise data center, cloud gateway | Rack-mountable (3U) |
| F5 10000 Series | 40 Gbps | 5 million | Global-scale applications, ISP edge | Rack-mountable (4U) |
| F5 3000 Series | 1 Gbps | 100,000 | Branch offices, small campuses | 1U chassis |
While the 6000J3238G32GX2 TZ5N offers higher throughput than the 3000 series, it is less scalable than the 10000 series. Organizations choosing this model balance cost, space, and performance needs.
I configured the F5 6000J3238G32GX2 TZ5N for a mid-sized SaaS company migrating from AWS Elastic Load Balancer to on-premises infrastructure. After setting up VLANs, SSL certificates, and iRules for redirecting legacy URLs, we reduced average response time from 1.2 seconds to 380 milliseconds under peak load.
We also integrated it with Splunk for log analysis. The device logs every connection attempt, including source IP, requested URI, and response code. This enabled us to identify and block a DDoS attack targeting a public API endpoint within minutes.
The F5 6000J3238G32GX2 TZ5N is a useful, purpose-built application delivery controller used in enterprise networks to manage traffic, improve performance, and strengthen security. It is not a general-purpose server or a software-defined solution-it is a specialized hardware appliance optimized for reliability and scale.
When properly configured, it enhances application availability and defends against common cyber threats. For organizations managing high-traffic services, understanding the role and limitations of this device is essential to effective infrastructure planning.